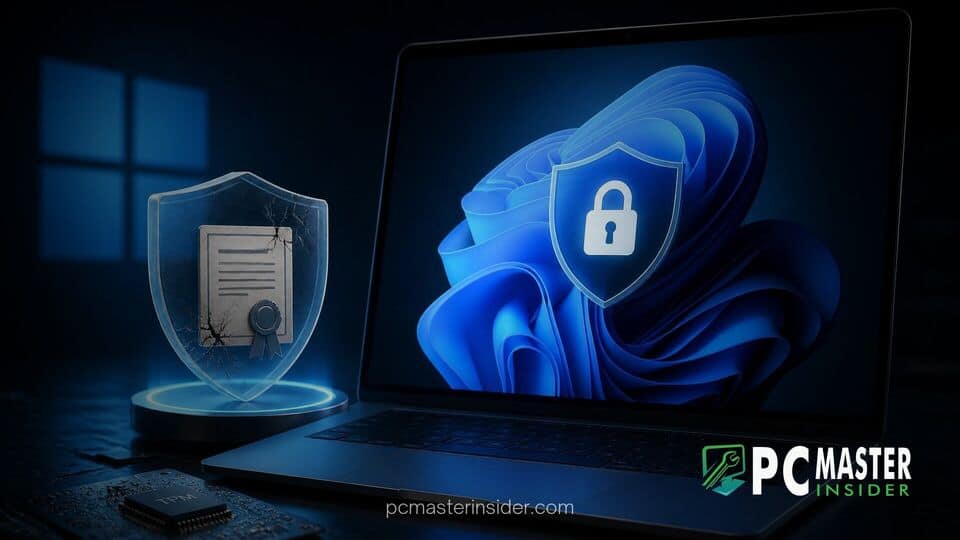
Microsoft has reached the final deadline in its multi-stage transition of legacy UEFI security infrastructure, marking the official expiration of the Microsoft Windows Production PCA 2011 certificate on October 19, 2026. While unpatched systems will not suddenly stop booting or experience immediate system crashes, failing to apply the updated 2023 security certificates will prevent devices from receiving future boot-level vulnerability protections.
The expiration event concludes a year-long phaseout of fifteen-year-old cryptographic assets that underpin the hardware trust chain across modern personal computers. Microsoft has released detailed technical guidance confirming that standard operating system functionality remains intact, but IT administrators and personal computer owners must ensure their devices possess the updated Windows UEFI CA 2023 certificates to maintain full early-boot protection.
windows 11 secure boot certificate expiration october 2026
The October 19, 2026 milestone specifically targets the primary root trust key used to sign the Windows Boot Manager software. Under the Secure Boot framework, UEFI firmware inspects digital signatures embedded within operating system bootloaders before handing off system execution. With the original 2011 certificate officially expired, future iterations of the Windows bootloader signed with replacement 2023 keys can only be validated on systems holding updated certificate databases.
Microsoft has clarified that systems missing the updated 2023 keys will continue to boot using existing, previously signed bootloaders and will still receive standard monthly cumulative updates. However, unupdated machines will no longer be eligible for critical security updates addressing early-boot vulnerabilities, including bootkit mitigations, revoking compromised boot components, and updating the Secure Boot allowed and blocked databases (DB and DBX).
Microsoft Reaches Final Secure Boot Certificate Deadline
The October deadline represents the third and final key expiration in Microsoft's overarching Secure Boot modernization initiative. The rollout began earlier in June 2026, when two subsidiary certificates expired in rapid succession:
- Microsoft Corporation KEK CA 2011: Expired on June 24, 2026. This Key Enrollment Key authorizes updates to the Secure Boot signature database (DB) and revocation list (DBX).
- Microsoft UEFI CA 2011: Expired on June 27, 2026. This certificate validates third-party bootloaders, EFI drivers, and expansion card Option ROMs.
- Microsoft Windows Production PCA 2011: Expired on October 19, 2026. This primary authority validates the Windows Boot Manager.
By transitioning systems to the newer Windows UEFI CA 2023 and Microsoft Corporation KEK 2K CA 2023 root trust stores, Microsoft aims to insulate operating systems against sophisticated hardware-level attacks and modern bootkit threats that attempt to execute code prior to Windows kernel startup.
Windows Production PCA 2011 Expiration Overview
Because the Windows Production PCA 2011 certificate directly validates the Windows boot process, its sunset required extensive cross-industry coordination between Microsoft, motherboard manufacturers, and enterprise device management vendors. For over a year, Microsoft has been staging certificate deployments through automatic Windows Update channels using high-confidence targeting logic.
Most managed enterprise systems and consumer PCs running supported software versions have already silently ingested the updated DB and KEK entries via regular servicing. Recent cumulative patches, including Windows 11 KB5127648, have continued automating certificate deployment across eligible desktop and server endpoints. However, devices with outdated motherboard firmware or misconfigured system hardware settings remain vulnerable to missing the replacement keys.
How Expiration Affects System Booting and Protection
A widespread misconception heading into the deadline was that machines running expired certificates would trigger blue screens or fail POST (Power-On Self-Test) sequences upon rebooting. Microsoft engineers explicitly addressed these concerns, confirming that existing signatures created prior to the expiration date remain cryptographically valid for boot validation.
The operational penalty for missing the 2023 certificates is exclusively related to future protection maintenance. Without updated keys stored in the motherboard's non-volatile memory (NVRAM), a system cannot trust newer Windows Boot Manager binaries released in subsequent operating system updates. Consequently, Microsoft will hold back early-boot updates from affected devices, leaving them running older, potentially vulnerable boot code.
Security features that depend on hardware-enforced boot integrity, such as BitLocker drive encryption, Credential Guard, and Virtualization-based Security (VBS), rely on up-to-date Secure Boot signatures to verify system health before unlocking sensitive enterprise data. Enterprise environments maintaining strict compliance standards may find non-updated machines failing remote attestation health checks.
Verification Steps and Firmware Update Recommendations
To verify whether a computer has successfully received the updated 2023 certificates, individual users can inspect their status directly inside Windows 11. Opening the Windows Security application, navigating to Device Security, and selecting Secure Boot will display the current certificate health status. Alternatively, system administrators can run PowerShell commands or utilize endpoint management dashboards like Microsoft Intune to query NVRAM certificate entries across enterprise fleets.
If a machine indicates that its Secure Boot certificate updates are pending or failed, Microsoft recommends the following remediation steps:
- Verify Windows Update Status: Ensure the operating system is updated with the latest cumulative security patches.
- Check UEFI/BIOS Firmware: Download and install the latest system BIOS updates from the original equipment manufacturer (OEM), as outdated system firmware can block Windows Update from writing to the system's Secure Boot NVRAM storage.
- Confirm Secure Boot State: Ensure Secure Boot is actively enabled in the motherboard firmware settings, as disabled systems cannot process certificate updates.
- Resolve Encryption Conflicts: Address any BitLocker or third-party disk encryption suspension prompts that might prevent writing to system boot variables.
System updates across Windows 11 continue to refine performance and system security, ranging from memory management enhancements boosting responsiveness to expanded authentication options like passwordless web sign-ins for Entra hybrid PCs. Ensuring underlying hardware trust platforms are updated guarantees these operating system safety features function without interruption.
In summary, while the passing of the October 19 deadline will not cause immediate startup failures, taking the time to verify UEFI Secure Boot certificate compliance ensures your Windows 11 PC remains fully protected against emerging boot-level security risks for years to come.